The State Bank of India (SBI) has informed customers whose personal information was identified in a recent data leak through email and WhatsApp. The country's largest public sector lender has reassured affected customers that their account balances and funds remain safe despite concerns over the suspected exposure of sensitive information.
In a statement, SBI said it had individually informed all customers whose data was identified as being involved in the cyber incident through email and/or WhatsApp. However, the bank did not disclose the exact number of customers who received the notifications.
The development comes after SBI identified 3,897 customer records containing personally identifiable information during a preliminary examination of approximately 3.75 lakh records found on the dark web. The bank had earlier disclosed the incident and initiated a detailed cybersecurity investigation.
What SBI Said About the Data Leak
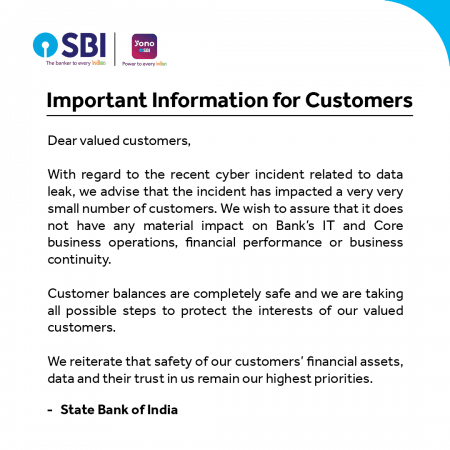
Reassuring customers about the safety of their money, SBI reiterated that the account balances and funds of affected customers remain secure. The bank also urged customers to follow safe digital banking practices and remain alert to potential fraud attempts.
SBI advised customers never to share their one-time passwords (OTPs), personal identification numbers (PINs) or passwords with anyone. It also cautioned them against suspicious phone calls, messages and emails that could be linked to fraudulent activities.
What Customer Information Was Exposed?
According to SBI's preliminary findings, the records identified on the dark web contained personal information, including customer names, registered mobile numbers, dates of birth, email addresses and residential addresses, along with loan-related information.
The bank is still investigating the authenticity, source and full extent of the suspected data exposure. The exact circumstances behind the incident and the potential risks to affected customers are yet to be established.
SBI Launches Cybersecurity Investigation
Following the incident, SBI activated its cybersecurity incident response procedures and appointed an independent cybersecurity agency empanelled with the Indian Computer Emergency Response Team (CERT-In) to investigate the matter.
The investigation aims to determine the nature and extent of the suspected exposure and identify its possible source. The bank has also maintained that the incident has not materially affected its core banking operations, financial performance or business continuity.
While SBI has reassured customers about the safety of their funds, the incident highlights the importance of protecting personal information and remaining vigilant against digital banking fraud. Customers are advised to verify suspicious communications through official bank channels and avoid sharing confidential banking credentials.