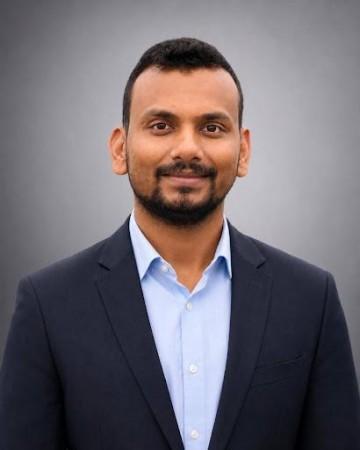
For Staff Engineer Satyam Nikhra, a consumer application can appear to be online and still fail at its most important task. A borrower may be unable to complete an application; a retried request may create a duplicate transaction; or personal information may travel farther through a system than the task requires. These failures rarely look like a dramatic outage, but they can undermine customer trust and the decisions a business makes from its data. Addressing these less visible failure modes is central to his work.
With almost a decade of industry experience, Nikhra has worked on platforms for consumer lending, advertising research and automotive retail, as well as enterprise access-management and healthcare-documentation systems. Across these settings, his work has connected application architecture with the practical demands of production: clear signals when a journey breaks, safeguards against inconsistent records, and controls over sensitive data.
Building a Reusable Foundation for Lending
The clearest recent example is his work on a consumer-lending application for student-loan refinancing and personal loans. It supports prospective borrowers as they provide information and learn the rates for which they may qualify. The previous application had become difficult to change: its application and backend layers were tightly coupled, testing was challenging, and engineers had limited visibility into its behavior in production.
The clearest recent example is his work on a consumer-lending application for student-loan refinancing and personal loans. It supports prospective borrowers as they provide information and learn the rates for which they may qualify. The previous application had become difficult to change: its application and backend layers were tightly coupled, testing was challenging, and engineers had limited visibility into its behavior in production.
Nikhra developed the initial proof of concept for a replacement and presented the modernization strategy to stakeholders. He then led the architecture and development of the new application. Instead of creating a one-off replacement for a single product, he designed a reusable foundation for multiple lending experiences and engineering teams. He defined architectural patterns, coding and implementation practices, observability, and security guardrails, and mentors engineers building on the platform.
The platform provides a shared foundation for borrower-facing application journeys across multiple lending products.
Making Reliability Observable
One of the changes Nikhra emphasized was observability. A service may report that it is healthy even while customers cannot complete a step. Monitoring designed around the application's behavior gives engineers a clearer way to identify where a journey stalls and to diagnose issues that were difficult to trace in the earlier system.
One of the changes Nikhra emphasized was observability. A service may report that it is healthy even while customers cannot complete a step. Monitoring designed around the application's behavior gives engineers a clearer way to identify where a journey stalls and to diagnose issues that were difficult to trace in the earlier system.
The same reliability principle applies to services supplied by outside vendors. In his DZone article, "The Hidden Production Risks of Third-Party SDKs," Nikhra describes why nonessential tools, such as analytics or support widgets, should be allowed to fail without taking a core customer journey with them. If analytics is unavailable, for example, checkout should still work. He argues that integrations need defined timeouts and fallback behavior so an external delay does not become a larger product incident.
Protecting the Meaning of Data
Earlier in his career, Nikhra worked on a production platform used to run standardized advertising-research studies. Participants viewed advertisements and answered structured questions; their responses formed the data used in the company's measurements. His work covered the survey flow, APIs, backend services, data stores and automated tests, and included helping modernize portions of the application.
Earlier in his career, Nikhra worked on a production platform used to run standardized advertising-research studies. Participants viewed advertisements and answered structured questions; their responses formed the data used in the company's measurements. His work covered the survey flow, APIs, backend services, data stores and automated tests, and included helping modernize portions of the application.
In that environment, consistency was part of the measurement itself. If an advertisement is presented inconsistently, or a response changes as it passes from the application to storage, the result may not appear as a system outage. It may instead appear as a finding about consumer behavior. The platform therefore had to preserve the conditions of the study as well as record its results.
Nikhra has also written about a related problem in distributed systems: duplicate requests. In his HackerNoon article, "Designing Idempotent APIs for Real-World Applications," he writes, "In distributed systems, duplicate requests are not rare edge cases. They are normal production behavior." A page refresh, a dropped connection or a replayed event can send the same request again. Client-side precautions can reduce accidental repeats, but he argues that the backend, as the system of record, must ensure that repeating a request does not repeat its effect. That principle is important wherever a duplicate payment, booking or application action would create confusion for customers and businesses.
In automotive retail, Nikhra worked on an online car-buying platform from its early stages. He designed its initial structure, contributed to its production deployment, implemented the unit-testing framework and set coding standards for the team. He also consolidated APIs and moved shared logic into backend services.
Limiting the Exposure of Personal Information
Consumer-lending applications handle personal and financial information from the start of a borrower's journey. The security guardrails Nikhra defined for the new platform were intended for a system carrying that responsibility.
Consumer-lending applications handle personal and financial information from the start of a borrower's journey. The security guardrails Nikhra defined for the new platform were intended for a system carrying that responsibility.
His published guidance makes the underlying principle explicit. In "Treat PII as Toxic: Designing Secure Systems That Contain the Blast Radius," published on DZone, he argues that personally identifiable information should be handled as hazardous material: collect only what is needed, keep it out of logs, limit its movement between services, protect it when stored, and audit access. He identifies logging full request payloads and sending personal information to third-party analytics tools as common sources of unnecessary exposure. His writing on vendor integrations applies the same idea at the boundary of a system: external services should receive only the information they require.
Research, Presentations, and Peer Review
At ETNCC 2026 in Windhoek, he presented research on API communication latency and throughput in full-stack systems. At AMLDS 2026 in Osaka, he presented a co-authored paper on a pattern-based approach to scalable web architecture integrating micro frontends and microservices. He has also reviewed submissions for international computing conferences.
At ETNCC 2026 in Windhoek, he presented research on API communication latency and throughput in full-stack systems. At AMLDS 2026 in Osaka, he presented a co-authored paper on a pattern-based approach to scalable web architecture integrating micro frontends and microservices. He has also reviewed submissions for international computing conferences.
Across these projects, Nikhra's focus is the infrastructure behind a customer's interaction: systems that can be observed when something goes wrong, preserve the meaning of the information they process, and limit the spread of sensitive data. For him, reliability is not only a matter of remaining online. It is also whether a retry stays safe, a response remains accurate, and personal information goes only where it is needed.